

In a shocking security revelation labeled as report 113887 hackers stole flock camera found 27321 video clips, sending shockwaves through privacy advocacy groups across the United States. This unprecedented physical breach of surveillance hardware has exposed severe vulnerabilities in how automated license plate recognition systems manage sensitive civilian data.
For years, companies supplying surveillance technology to law enforcement have promised ironclad data protection. However, the details emerging from the event where 113887 hackers stole flock camera found 27321 video clips completely contradict those corporate assurances. The physical theft and subsequent reverse engineering of the device revealed an alarming trove of retained data that was supposedly temporary.
As cities race to understand the implications of this Flock camera privacy breach, technical investigations are uncovering exactly what was hidden inside the Android-based hardware. The findings have ignited fierce debates over mass surveillance and data retention limits.
The Stegan0gram Heist: 113887 hackers stole flock camera found 27321 video clips
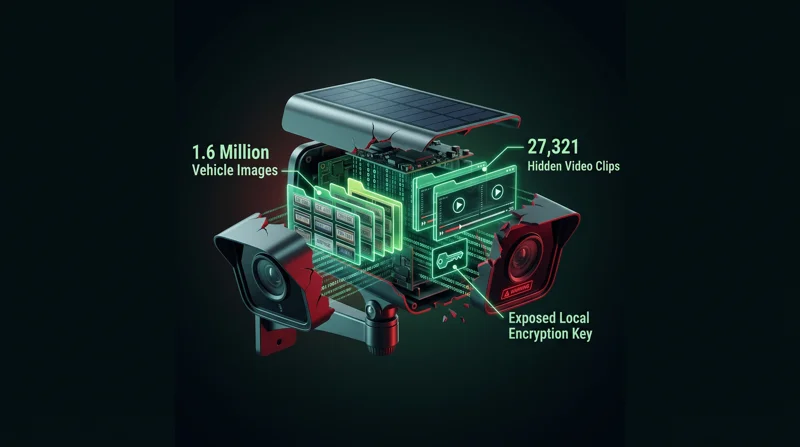
The incident began when the Stegan0gram hacker group physically pulled down and disarmed a solar-powered camera situated above a public roadway. Rather than executing a remote cloud breach, the group physically compromised the hardware. Their investigation into the device’s unencrypted storage partitions led to the discovery that 113887 hackers stole flock camera found 27321 video clips stored locally.
More concerning than the video files was the sheer volume of still imagery. The hackers extracted roughly 1.6 million images of 50,200 unique vehicles spanning just 21 days. This massive Flock surveillance footage storage capacity proved that the cameras retain highly detailed logs of civilian movements for extended periods.
Furthermore, the group discovered an ALPR data encryption key resting directly on one of the device’s unencrypted partitions. This critical security failure allowed them to unlock deeper areas of the hardware containing the recorded MP4 media files, exposing the fragile nature of the camera’s local security protocols.
| Data Type Discovered | Quantity / Details | Security Status |
|---|---|---|
| Still Images | 1.6 Million (50,200 vehicles) | Found in system logs |
| Video Files (MP4) | 27,321 clips (1024 x 768 res) | Unlocked via local key |
| Security Credentials | 1 Local Encryption Key | Left on unencrypted partition |
“Finding an encryption key sitting in plain text on an unencrypted partition defeats the entire purpose of securing the recorded surveillance media.”
Contradicting Claims in Case 113887 hackers stole flock camera found 27321 video clips
Flock license plate readers have historically been marketed with strict privacy reassurances. The company previously claimed that physical access to a unit would not expose captured footage because the images were briefly held and swiftly uploaded to secure servers. However, the reality that 113887 hackers stole flock camera found 27321 video clips shatters this narrative.
The camera was found holding tens of thousands of errors indicating it was trying to save full-resolution images even when its local storage was full. This suggests the hardware actively hoards data locally, creating a lucrative target for bad actors. The software also actively detected people, spotting motorcyclists in several clips, and mistakenly logged bumper stickers and American flag patches as license plates.
These revelations are proving disastrous for the company’s public relations and municipal contracts. The situation surrounding the report 113887 hackers stole flock camera found 27321 video clips is giving civil rights advocates exactly what they need to challenge these systems.
Municipal Backlash: 113887 hackers stole flock camera found 27321 video clips
The fallout from this Flock camera privacy breach is accelerating an already growing trend: US cities are dropping the surveillance technology. Following reports of police officers using the system to stalk former partners or entering nonsense justifications to search databases, public trust is at an all-time low.
As detailed in the event where 113887 hackers stole flock camera found 27321 video clips, leaving a decryption key locally accessible represents a fundamental design flaw. Privacy experts argue that a system designed to monitor public roadways must utilize end-to-end encryption without local key storage.
| Corporate Claim | Hacker Discovery | Privacy Impact |
|---|---|---|
| Data is deleted immediately post-upload | Weeks of data retained on local storage | High physical theft risk |
| Hardware is highly secure | Unencrypted partition with encryption key | Total compromise of local media |
| Reads plates only | Detected humans and recorded 27,000 videos | Unwarranted public surveillance |
“When municipalities realize their residents’ daily routines are sitting unencrypted on a roadside pole, the debate shifts from security to outright privacy invasion.”
The Future of Surveillance After 113887 hackers stole flock camera found 27321 video clips
Flock’s official response to the controversy was defensive, stating that tampering with their hardware is illegal while claiming they lacked sufficient details from the Stegan0gram hacker group to assess the vulnerability. For more context on surveillance guidelines and citizen rights, you can consult resources from the Electronic Frontier Foundation.
Despite corporate pushback, the undeniable proof that 113887 hackers stole flock camera found 27321 video clips will serve as a permanent case study in cybersecurity failures. Until hardware manufacturers drastically alter how they handle ALPR data encryption key management and Flock surveillance footage storage, public roadways remain vulnerable to physical data heists.
Frequently Asked Questions

What exactly happened in the incident where 113887 hackers stole flock camera found 27321 video clips?
A hacker group named Stegan0gram physically stole a Flock surveillance camera, reverse-engineered it, and found 1.6 million images and over 27,000 video clips stored locally, alongside an encryption key.
Who is the Stegan0gram hacker group?
They are a collective of hackers and security researchers who physically disarmed and analyzed the Flock camera to expose its underlying data retention flaws.
Did the hackers breach Flock’s cloud network?
No, the entire investigation was conducted locally on the stolen physical hardware, proving that the devices themselves hoard massive amounts of sensitive data.
Why is the ALPR data encryption key discovery a big deal?
The hackers found the key on an unencrypted partition of the camera, which allowed them to easily unlock the restricted areas containing the thousands of MP4 video clips.
Did the camera record audio with the videos?
No, the 27,321 MP4 video clips, which were mostly one to two seconds long and at 1024 x 768 resolution, did not contain any audio tracks.
How is Flock responding to the 113887 hackers stole flock camera found 27321 video clips report?
Flock responded by stating that unauthorized physical tampering with their cameras is illegal and claimed they had not received a formal vulnerability report through proper channels.
Why are cities canceling contracts with Flock?
Alongside this severe data exposure, there have been numerous instances of police abusing the system to stalk individuals, leading many municipalities to reconsider the privacy costs of the technology.
Disclaimer: This article is for informational purposes only. The events described are based on third-party cybersecurity reports and journalistic investigations regarding hardware vulnerabilities and data privacy.